Ignite Realtime Blog: New Openfire plugin: Reporting Account Affiliations
I’m excited to announce a new Openfire plugin: the Reporting Account Affiliations Plugin!
This plugin implements a new prototype XMPP extension of the same name.
To quote the specification:
In practice, a server may not trust all accounts equally. For example, if a server offers anonymous access or open registration, it … ⌘ Read more
How to Use & Access GPT-4 for Free
You may already be using ChatGPT, the phenomenally powerful and useful AI tool, but the free version is based on GPT-3.5. GPT-4 is said to be ten times more advanced, with enhanced creativity, reliability, up-to-date information, and an ability to interpret more nuanced instructions, so it’s understandable why users would like to explore and experience … Read More ⌘ Read more
Having fun with React - yet again. A large part of my job entails (re)learning technologies - luckily I have access to some good resources in the form of training- and tutorial sites, all provided by my employer.
Starlink and Natural Monopolies
A couple of weeks ago Elon Musk tweeted (or Xed, or whatever it’s called today) that Starlink has broken even and congratulated its team. The company has been offering fast satellite internet access through its own Low Earth Orbit (LEO) constellation of more than 5000 satellites. As part of SpaceX, it’s the first company of […] ⌘ Read more
Worked on expanding the scope of accessible alternative press in my RSS aggregator. The numbers reached were 215 media.
Diversity, inclusion, and belonging at GitHub in 2023
We expanded diversity of our employee base, launched several new employee engagement programs, made investments to improve accessibility, and more.
The post Diversity, inclusion, and belonging at GitHub in 2023 appeared first on The GitHub Blog. ⌘ Read more
5 tips for making your GitHub profile page accessible
Your profile’s README invites the world to know you and your work, so it’s important that everyone can read and understand it. In this post, we share some tips for making your README more accessible.
The post 5 tips for making your GitHub profile page accessible appeared first on The GitHub Blog. ⌘ Read more
How to Recover Recently Deleted Passwords on Mac
Forgetting or losing a password is a hassle, but assuming you save your logins and passwords with iCloud Keychain, that happens less and less. But you can still delete a password or login, whether intentionally or accidentally, and then end up needing access to that login information or password later. Fortunately the Mac offers a … Read More ⌘ Read more
Your curated GitHub Universe agenda: AI, ethics, and productivity
Gain actionable insights about the intersection of AI and human skills, while tackling ethics, accessibility, and productivity at these GitHub Universe sessions.
The post Your curated GitHub Universe agenda: AI, ethics, and productivity appeared first on The GitHub Blog. ⌘ Read more
How to “Save As” in MacOS Sonoma & Ventura
Do you wish you had the “Save As” keyboard shortcut back in MacOS Sonoma and MacOS Ventura? Wish no more, it’s easy to re-enable, even in the latest versions of MacOS system software and with the peculiar System Settings experience. Many longtime Mac users adore the “Save As” keyboard shortcut, which had been accessed by … Read More ⌘ Read more
I’m telling ya guys 😅 plex.tv had way better shit™, Get it installed on your own server, get access to free content + your own + whatever and no stupid tracking and bullshit 🤣
Prompting GitHub Copilot Chat to become your personal AI assistant for accessibility
GitHub Copilot Chat can help you learn about accessibility and improve the accessibility of your code. In this blog, we share a sample foundational prompt that instructs GitHub Copilot Chat to become your personal AI assistant for accessibility.
The post [Prompting GitHub Copilot Chat to become your personal AI assistant for accessibility](https://github.blog/2023-10- … ⌘ Read more
Announcing Udemy + Docker Partnership
Docker and Udemy announced a new partnership at DockerCon to give developers a clear, defined, accessible path for learning how to use Docker, best practices, advanced concepts, and everything in between. As the #1 rated online course platform (as ranked by Stack Overflow), Udemy will be the first to house Docker-accredited content and customized learning paths to provide developers with the latest training materials on how to best use Docker tools. ⌘ Read more
How to Install iOS 17 on iPhone
Installing iOS 17 onto your iPhone is easy to do, and you’ll gain access to the neat new features available in iOS 17. This includes everything from customizable contact cards, FaceTime Video voicemail, interactive widgets on your Home Screen, NameDrop easy contact sharing, new stickers features in Messages, new ringtones and text tones, new autocorrect … Read More ⌘ Read more
How I used GitHub Copilot Chat to build a ReactJS gallery prototype
GitHub Copilot Chat can help developers create prototypes, understand code, make UI changes, troubleshoot errors, make code more accessible, and generate unit tests.
The post How I used GitHub Copilot Chat to build a ReactJS gallery prototype appeared first on The GitHub Blog. ⌘ Read more
Changes to How Docker Handles Personal Authentication Tokens
Docker is improving the visibility of Docker Desktop and Hub users’ personal access tokens. Specifically, we are changing how tokens are handled across sessions between the two tools. Learn more about this security improvement. ⌘ Read more
GitHub Copilot Chat beta now available for all individuals
All GitHub Copilot for Individuals users now have access to GitHub Copilot Chat beta, bringing natural language-powered coding to every developer in all languages.
The post GitHub Copilot Chat beta now available for all individuals appeared first on The GitHub Blog. ⌘ Read more
Hardening repositories against credential theft
Some best practices and important defenses to prevent common attacks against GitHub Actions that are enabled by stolen personal access tokens, compromised accounts, or compromised GitHub sessions.
The post Hardening repositories against credential theft appeared first on The GitHub Blog. ⌘ Read more
Docker Desktop 4.22: Resource Saver, Compose ‘include’, and Enhanced RBAC Functionality
Docker Desktop 4.22 is now available, with improved memory & CPU management, support for Compose subprojects, and improvements to role-based access control. ⌘ Read more
GitHub Copilot Chat beta now available for every organization
All GitHub Copilot for Business users now have access to a limited GitHub Copilot Chat beta, bringing the power of conversational coding right to the IDE. ⌘ Read more
Erlang Solutions: How IoT is Revolutionising Supply Chain Management
As global supply chains continue to face significant disruptions, many businesses are turning to IoT to access greater visibility, reactivity, and streamlined operations.
Unforeseen geopolitical conflicts, economic pressures due to inflation and severe climate change events have all contributed to an uncertain and cost … ⌘ Read more
Isode: Icon-PEP 2.0 – New Capabilities
Icon-PEP is used to enable the use of IP applications over HF networks. Using STANAG 5066 Link Layer as an interface.
Listed below are the changes brought in with 2.0.
Web ManagementA web interface is provided which includes:
- Full configuration of Icon-PEP
- TLS (HTTPS) access and configuration including bootstrap with self signed certificate and ide … ⌘ Read more
↳
In-reply-to
»
why am I not surprised?… https://uk.pcmag.com/ai/147757/elon-musk-will-train-his-ai-project-using-your-tweets
⤋ Read More
no wonder he cut off API access and added rate limit.
(De)coding conventions
Navigating the ebb and flow of programming paradigms–from the shifts in the JavaScript ecosystem and TypeScript’s rise, to AI’s role in advancing accessibility, and strategies for encouraging non-code contributions–tune in to the latest episode of The ReadME Podcast for more. ⌘ Read more
Accessibility considerations behind code search and code view
A look at how we improved the readability of code on GitHub. ⌘ Read more
Question to all you Gophers out there: How do you deal with custom errors that include more information and different kinds of matching them?
I started with a simple var ErrPermissionNotAllowed = errors.New("permission not allowed"). In my function I then wrap that using fmt.Errorf("%w: %v", ErrPermissionNotAllowed, failedPermissions). I can match this error using errors.Is(err, ErrPermissionNotAllowed). So far so good.
Now for display purposes I’d also like to access the individual permissions that could not be assigned. Parsing the error message is obviously not an option. So I thought, I create a custom error type, e.g. type PermissionNotAllowedError []Permission and give it some func (e PermissionNotAllowedError) Error() string { return fmt.Sprintf("permission not allowed: %v", e) }. My function would then return this error instead: PermissionNotAllowedError{failedPermissions}
At some layers I don’t care about the exact permissions that failed, but at others I do, at least when accessing them. A custom func (e PermissionNotAllowedError) Is(target err) bool could match both the general ErrPermissionNotAllowed as well as the PermissionNotAllowedError. Same with As(…). For testing purposes the PermissionNotAllowedError would then also try to match the included permissions, so assertions in tests would work nicely. But having two different errors for different matching seems not very elegant at all.
Did you ever encounter this scenario before? How did you address this? Is my thinking flawed?
Introduction to SELinux
SELinux is the most popular Linux Security Module used to isolate and protect system components from one another. Learn about different access control systems and Linux security as I introduce the foundations of a popular type system. ⌘ Read more
An official FBI document dated January 2021, obtained by the American association “Property of People” through the Freedom of Information Act.
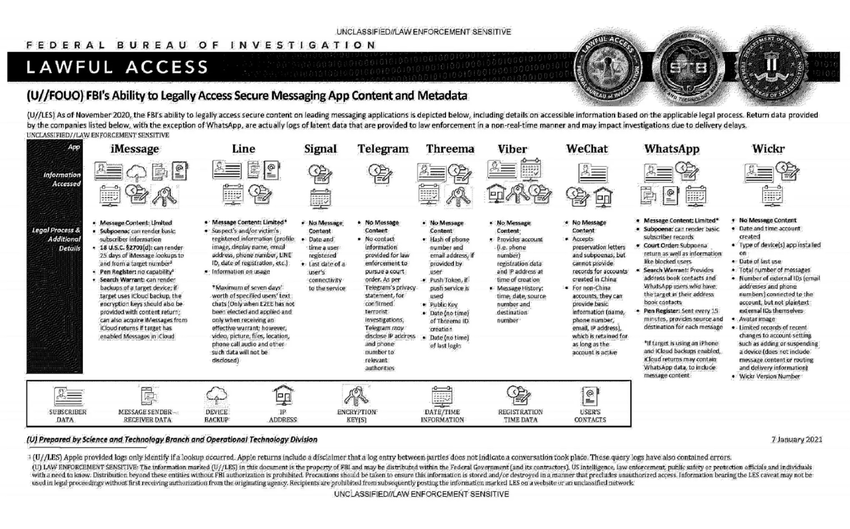
This document summarizes the possibilities for legal access to data from nine instant messaging services: iMessage, Line, Signal, Telegram, Threema, Viber, WeChat, WhatsApp and Wickr. For each software, different judicial methods are explored, such as subpoena, search warrant, active collection of communications metadata (“Pen Register”) or connection data retention law (“18 USC§2703”). Here, in essence, is the information the FBI says it can retrieve:
Apple iMessage: basic subscriber data; in the case of an iPhone user, investigators may be able to get their hands on message content if the user uses iCloud to synchronize iMessage messages or to back up data on their phone.
Line: account data (image, username, e-mail address, phone number, Line ID, creation date, usage data, etc.); if the user has not activated end-to-end encryption, investigators can retrieve the texts of exchanges over a seven-day period, but not other data (audio, video, images, location).
Signal: date and time of account creation and date of last connection.
Telegram: IP address and phone number for investigations into confirmed terrorists, otherwise nothing.
Threema: cryptographic fingerprint of phone number and e-mail address, push service tokens if used, public key, account creation date, last connection date.
Viber: account data and IP address used to create the account; investigators can also access message history (date, time, source, destination).
WeChat: basic data such as name, phone number, e-mail and IP address, but only for non-Chinese users.
WhatsApp: the targeted person’s basic data, address book and contacts who have the targeted person in their address book; it is possible to collect message metadata in real time (“Pen Register”); message content can be retrieved via iCloud backups.
Wickr: Date and time of account creation, types of terminal on which the application is installed, date of last connection, number of messages exchanged, external identifiers associated with the account (e-mail addresses, telephone numbers), avatar image, data linked to adding or deleting.
TL;DR Signal is the messaging system that provides the least information to investigators.
An official FBI document dated January 2021, obtained by the American association “Property of People” through the Freedom of Information Act.
This document summarizes the possibilities for legal access to data from nine instant messaging services: iMessage, Line, Signal, Telegram, Threema, Viber, WeChat, WhatsApp and Wickr. For each software, different judicial methods are explored, such as subpoena, search warrant, active collection of communications metadata (“Pen Register”) or connection data retention law (“18 USC§2703”). Here, in essence, is the information the FBI says it can retrieve:
Apple iMessage: basic subscriber data; in the case of an iPhone user, investigators may be able to get their hands on message content if the user uses iCloud to synchronize iMessage messages or to back up data on their phone.
Line: account data (image, username, e-mail address, phone number, Line ID, creation date, usage data, etc.); if the user has not activated end-to-end encryption, investigators can retrieve the texts of exchanges over a seven-day period, but not other data (audio, video, images, location).
Signal: date and time of account creation and date of last connection.
Telegram: IP address and phone number for investigations into confirmed terrorists, otherwise nothing.
Threema: cryptographic fingerprint of phone number and e-mail address, push service tokens if used, public key, account creation date, last connection date.
Viber: account data and IP address used to create the account; investigators can also access message history (date, time, source, destination).
WeChat: basic data such as name, phone number, e-mail and IP address, but only for non-Chinese users.
WhatsApp: the targeted person’s basic data, address book and contacts who have the targeted person in their address book; it is possible to collect message metadata in real time (“Pen Register”); message content can be retrieved via iCloud backups.
Wickr: Date and time of account creation, types of terminal on which the application is installed, date of last connection, number of messages exchanged, external identifiers associated with the account (e-mail addresses, telephone numbers), avatar image, data linked to adding or deleting.
TL;DR Signal is the messaging system that provides the least information to investigators.
Isode: Harrier 3.3 – New Capabilities
Harrier is our Military Messaging client. It provides a modern, secure web UI that supports SMTP, STANAG 4406 and ACP 127. Harrier allows authorised users to access role-based mailboxes and respond as a role within an organisation rather than as an individual.
 to support mand … ⌘ Read more
In reply to: Oatmeal - week notes
The worst kind of blogging is blogging about blogging, so, I’ll keep this blogging about blogging short!
I’ve made some minor updates to the design of the website that have improved it’s usability a wee bit, and are a step in the right direction toward upping my accessibility game. The major remaining accessibility issues are around color contrast and some structura … ⌘ Read more
The most secure way to access this site is to torify a gopher client and go to the onion address.
Dependabot alerts are now visible to more developers
Default settings will allow developers with write and maintain access to see and resolve Dependabot alerts. ⌘ Read more
↳
In-reply-to
»
And in the latest "don't store your passwords in the cloud" news, NortonLifeLock warns that hackers breached Password Manager accounts
⤋ Read More
@xuu@txt.sour.is yeah, I know less about ISO27k (in part because you have to pay for access to the complete standards documents!!!), but I figured it was similar.
I had an AWS training in November and have the opportunity to get the “Certified Developer Associate” certificate. Even though I have two attempts, I want to do well on the first shot. Since the trainer didn’t show us everything that is required for the exam, I’m kind of re-doing the training with this Udemy course (luckily I have access to Udemy Business and don’t have to pay for it). It’s really helpful because it helps me demystify the AWS cloud and reduce the 🤯 whenever I do something in the AWS console. ⌘ Read more
Pourquoi ChatGPT n’est pas qu’une intéressante curiosité
Le 30 novembre 2022 est une date à garder en tête : c’est ce jour que ChatGPT est officiellement devenu accessible à tous. ChatGPT a été produit par OpenAI, une société créée en 2015 et qui s’est lancée dans l’intelligence artificielle. En janvier 2021, elle proposait déjà Dall-E, un modèle de traitement du langage entraîné sur […] ⌘ Read more
I bought a full year of access to the Freeletics coach, so I should actually start doing my workout, right? 🙃 I can already feel the soreness just thinking about it… ⌘ Read more
I couldn’t access the Pleroma link.
Anyone uses the putr command? (to access pdp11 disk images)
** Thoughts on accessibility in smol computing **
What follows is my attempt to spark a conversation in a few converging, but separate communities I lurk in.
I’ve already had a bunch of amazing conversations around this topic with a lot of people. Those conversations helped to shape what follows. Thanks to everyone who was willing to think this stuff through with me.
Before I get into it I want to say at the top this isn’t meant as an accusation against anyone in these communities, nor the goals of t … ⌘ Read more
Creating an accessible search experience with the QueryBuilder component
GitHub’s search inputs have several complex accessibility considerations. Let’s dive into what those are, how we addressed them, and talk about the standalone, reusable component that was ultimately built. ⌘ Read more
The Tandy Zoomer – The x86 PDA before the Palm Pilot
A 1992 handheld, with multitasking, that could access AOL. Wild. ⌘ Read more
The Laws of OAuth
The first law of OAuth states that the total number of authorized access tokens must remain constant in an isolated system. ⌘ Read more
GitHub, accessibility, and the disability divide
We just published our vision for GitHub accessibility at accessibility.github.com. Here’s the TL;DR: the prime directive of the GitHub accessibility program is to empower people with disabilities to build cool technology. ⌘ Read more
Erlang Solutions: Advent of Code 2022 – Every Puzzle Solved in Erlang
Day 1Christmas is getting closer and with that, the annual Advent of Code begins. For those who do not know, Advent of Code is a fun and inclusive event which provides a new programming puzzle every day. The fun is that these puzzles can be solved in any programming language and are accessible for varying levels of coding experience and skills. The real test is in your problem-solving. This year, we’ll be solving each of the problems in … ⌘ Read more
JMP: Writing a Chat Client from Scratch
There are a lot of things that go into building a chat system, such as client, server, and protocol. Even for only making a client there are lots of areas of focus, such as user experience, features, and performance. To keep this post a manageable size, we will just be building a client and will use an existing server and protocol (accessing Jabber network services using the XMPP protocol). We’ll make a practical GUI so we can test things, but not spend too much time on p … ⌘ Read more
RT by @mind_booster: The EU will fund a pilot project for a public directory of #publicdomain works. This is based on a whitepaper I wrote with @Senficon for the 2021 @creativecommons summit. Thanks for bringing us 1 step closer to making this a reality @echo_pbreyer & team! https://www.patrick-breyer.de/en/kick-off-for-eu-database-of-public-domain-works-and-digital-access-to-scientific-works/
The EU will fund a pilot project for a public directory of [#publicdomain](https://nitter.net/search?q=%23publicdom … ⌘ Read more
Jérôme Poisson: Libervia progress note 2022-W45
Hello, it’s time for a long overdue progress note.
I’ll talk here about the work made on ActivityPub (AP) gateway and on end-to-end encryption around pubsub.
Oh, and if everything goes well, this blog post should be accessible from XMPP and ActivityPub (and HTTP and ATOM feed), using the same identifier goffi@goffi.org.
The work made on the AP gateway has been possible thanks to a NLnet/NGI0 grant (w … ⌘ Read more
Tried to pull down the latest yarn, but I get this:
unable to access ‘https://git.mills.io/yarnsocial/yarn/’: server certificate verification failed. CAfile: /etc/ssl/certs/ca-certificates.crt CRLfile: none
Not sure if the issue is on my end or the other..
↳
In-reply-to
»
Atom vs. RSS: https://mckinley.cc/blog/20221109.html
⤋ Read More
@mckinley@twtxt.net Thank you! I didn’t even know about signing and encrypting XML documents. Right, RSS is a little bit messy.
Unfortunately, the autodiscovery document in one of your linked resources does not exist anymore. What annoys me in Atom is the distinction between <id> and <link>. I always want my URL also to be my ID, so I have to duplicate that – unnecessarily in my opinion.
Also, never found a good explanation why I should add <link rel="self" … /> to my feeds. I just do, but I don’t understand why. The W3C Feed Validation Service says:
[…] This value is important in a number of subscription scenarios where often times the feed aggregator only has access to the content of the feed and not the location from which the feed was fetched.
This just sounds like a very questionable bandaid to bad software architecture. Why would the feed parser need access to the feed URL at this stage? And if so, why not just pass down the input source? Just doesn’t make sense to me.
Also, I just noticed that I reference the http://purl.org/rss/1.0/modules/syndication/ namespace, but don’t use it in most of my feeds. Gotta fix that. Must have copied that from my yfav feed without paying attention what I’m doing.
Your article made me reread the Atom spec and I found out, that I can omit the <author> in the <entry> when I specify a global <author> at <feed> level. Awesome! Will do that as well and thus reduce the feed size.
Improving navigation for GitHub Actions
GitHub Actions changed how developers automate workflows with GitHub. Today, we’re introducing a new navigation to manage your GitHub Actions experience, improving discoverability and accessibility as well as opening up future feature opportunities. ⌘ Read more
Introducing fine-grained personal access tokens for GitHub
Fine-grained personal access tokens offer enhanced security to developers and organization owners, to reduce the risk to your data of compromised tokens. ⌘ Read more
RT by @mind_booster: When it comes to improving access to AV works, the EU must — at the minimum — put an end to #geoblocking of publicly funded AV works. Here is our proposal that we have submitted to the @DigitalEU stakeholder dialogue last week: https://communia-association.org/2022/09/30/proposal-av-stakeholder-dialogue-geoblocking/
When it comes to improving access to AV works, the EU must — at the minimum — put an end to #geoblocking of publicly funded AV w … ⌘ Read more
GitHub supports internet freedom and global availability in Iran
Access to the open internet is essential to defending human rights, and developers have an important role in promoting freedom of expression and transparency. GitHub is committed to keeping Iranians connected to the global developer community. ⌘ Read more
September Extensions Roundup: Test APIs, Use Oracle SQLcl, and More
Find out what’s new this month in the Docker Extension Marketplace! Access InterSystems, test APIs, use Oracle SQLcl, and backup/share volumes — right from Docker Desktop. ⌘ Read more
wsl-vpnkit: Internet for WSL2 distros behind a VPN
I’m still alive. 👋 Today, at work, I discovered a nice little tool for WSL2. On my work laptop I need to use Cisco AnyConnect to connect to the corporate network. Unfortunately this blocks Internet access in Windows Subsystem for Linux VMs (at least in the Ubuntu VM, I tried to use for some Docker stuff). I tried a lot of different hacks and workarounds, but none worked. Until I found wsl-vpnkit. It just works. 😄 ⌘ Read more
Now that I have access to Udemy Business and can watch many, many courses for free, I subscribed to two courses. One to improve my English and one to improve my quick-wittedness. Let’s see if I complete them and if they really help. ⌘ Read more
Paul Schaub: Creating a Web-of-Trust Implementation: Accessing Certificate Stores
Currently, I am working on a Web-of-Trust implementation for the OpenPGP library PGPainless. This work is being funded by the awesome NLnet foundation through NGI Assure. Check them out! NGI Assure is made possible with financial support from the European Commission’s Next Generation Internet programme.
[
Content-Security-Policy: default-src 'none'; sandbox
Referrer-Policy: same-origin
Vary: Authorization
BEGIN:VCALENDAR
VERSION:2.0;2.0
PRODID:SandCal
CALSCALE:GREGORIAN
BEGIN:VEVENT
DTSTAMP:20220822T180903Z
UID:bb63bfbd-623e-4805-b11b-3181d96375e6
DTSTART;TZID=America/Chicago:20220827T000000
CREATED:20220822T180903Z
LAST-MODIFIED:20220822T180903Z
LOCATION:https://meet.jit.si/Yarn.social
SUMMARY:Yarn Call
RRULE:FREQ=WEEKLY
DTEND;TZID=America/Chicago:20220827T010000
END:VEVENT
END:VCALENDAR
↳
In-reply-to
»
@prologic I think we could use deltachats new decentralising app format for it: https://delta.chat/en/2022-06-14-webxdcintro
⤋ Read More
Huh… Nope.
HTTP/1.1 200 OK
Content-Length: 407
Content-Type: text/calendar
Access-Control-Allow-Origin: *
Access-Control-Expose-Headers: ETag
Permissions-Policy: interest-cohort=()
Content-Security-Policy: default-src 'none'; sandbox
Referrer-Policy: same-origin
Vary: Authorization


BEGIN:VCALENDAR
VERSION:2.0;2.0
PRODID:SandCal
CALSCALE:GREGORIAN
BEGIN:VEVENT
DTSTAMP:20220822T180903Z
UID:bb63bfbd-623e-4805-b11b-3181d96375e6
DTSTART;TZID=America/Chicago:20220827T000000
CREATED:20220822T180903Z
LAST-MODIFIED:20220822T180903Z
LOCATION:https://meet.jit.si/Yarn.social
SUMMARY:Yarn Call
RRULE:FREQ=WEEKLY
DTEND;TZID=America/Chicago:20220827T010000
END:VEVENT
END:VCALENDAR
Tailscale SSH
I finally got around to using Tailscale SSH. I’ve been using Tailscale for over a year to access my servers via SSH (my VPS is even available via Tailscale only), but I haven’t used the new Tailscale SSH feature yet. ⌘ Read more
Dependabot now alerts for vulnerable GitHub Actions
GitHub Actions gives teams access to powerful, native CI/CD capabilities right next to their code hosted in GitHub. Starting today, GitHub will send a Dependabot alert for vulnerable GitHub Actions, making it even easier to stay up to date and fix security vulnerabilities in your actions workflows. ⌘ Read more
All GitHub Enterprise users now have access to the security overview
Today, we’re expanding access to the GitHub security overview! All GitHub Enterprise customers now have access to the security overview, not just those with GitHub Advanced Security. Additionally, all users within an enterprise can now access the security overview, not just admins and security managers. ⌘ Read more
‘Based’ Paganism vs. Christianity
I’ve been meaning to write about Paganism recently. I will frame it as a response to an email I received within the past day or so:
Hey Luke,
First off, I would like to thank you for all your efforts in making everything
you know accessible to everyone. You have exposed me to some of the most
thought-provoking people on the internet and Varg is one of them. I was
wondering if you can write an article or make a video on what you think about
Varg’s Paganism in r … ⌘ Read more
Corrupting memory without memory corruption
In this post I’ll exploit CVE-2022-20186, a vulnerability in the Arm Mali GPU kernel driver and use it to gain arbitrary kernel memory access from an untrusted app on a Pixel 6. This then allows me to gain root and disable SELinux. This vulnerability highlights the strong primitives that an attacker may gain by exploiting errors in the memory management code of GPU drivers. ⌘ Read more
6 strategic ways to level up your CI/CD pipeline
From incorporating accessibility testing to implementing blue-green deployment models, here are six practical and strategic ways to improve your CI/CD pipeline. ⌘ Read more